


Blog
China-Linked Hackers Use AI to Target Korean Foreign Policy Organizations: What You Need to Know
17 November 2026
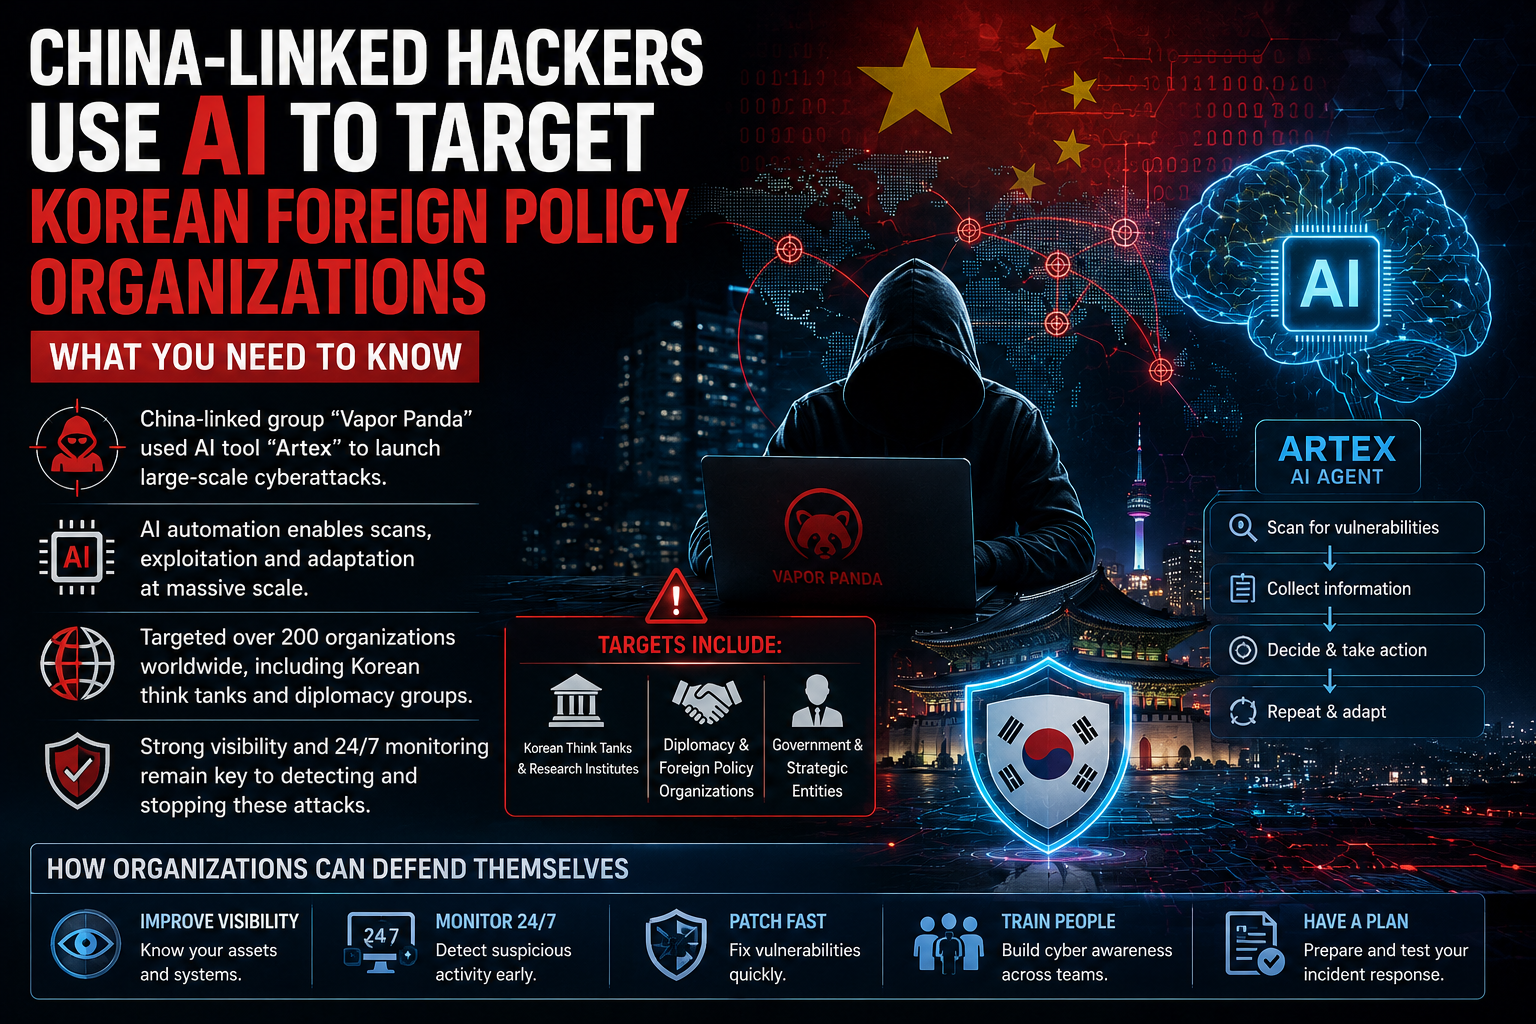
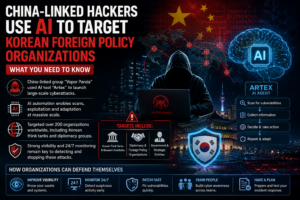
A China-linked hacking group called Vapor Panda used an AI-driven attack tool named Artex to go after organizations worldwide, including Korean think tanks and diplomacy-focused groups. According to cybersecurity firm CrowdStrike, some of the Korean intrusions worked. The bigger lesson is that AI has made existing hacking methods faster and cheaper to run at scale. Strong visibility and round-the-clock monitoring can still catch them.
What Happened: The Short Version
On Tuesday, November 17, 2026, a senior CrowdStrike executive told Korean reporters in an online briefing that his team had seen several Korea-related targets in a recent campaign. The company attributes the activity to Vapor Panda, a group linked to China.
Adam Meyers, who leads counter adversary operations at CrowdStrike, said the victims included research institutes and organizations working on Korean diplomacy and foreign policy. He confirmed that a number of the attempts succeeded. He did not name the organizations or describe how much damage was done. He did say that the affected parties and the relevant incident response authorities had been informed.
This Korea-focused update builds on an earlier CrowdStrike disclosure. On November 4, the company reported that the same group had gone after more than 200 organizations across the globe.
Who Is Vapor Panda?
Vapor Panda is a hacking group that CrowdStrike has followed since 2021. Over those years, the firm has studied its attack infrastructure, malware, web shells and choice of victims. In other words, this is not a newcomer. Meyers described it as an already skilled operation.
What changed is the toolkit. By adding AI automation, the group now appears able to hit hundreds of targets at the same moment, something that once required far more people and time.
Meet Artex: The AI Agent Behind the Campaign
The centerpiece of the operation is Artex, an AI agent built for penetration testing. Penetration testing is normally a defensive practice in which security professionals probe their own systems for weaknesses. Here, attackers turned that idea around.
Artex works in a loop:
- It scans web applications and APIs again and again, searching for weak spots.
- It collects information from each scan.
- It uses what it learned to decide on and launch the next step on its own.
No human needs to guide every move. The software keeps going, adapting at each stage based on what it finds.
CrowdStrike says Vapor Panda mainly relied on the Chinese AI model DeepSeek to power Artex. The group may also have used paid access to other advanced AI models as extra helpers.
The Global Scale of the Campaign
The earlier CrowdStrike report put the wider campaign between October 17 and October 29. During that window, the attackers reportedly went after:
- Diplomatic and security agencies in Latin America, Europe, Asia and the Middle East
- U.S. companies in pharmaceuticals, semiconductors, defense, nuclear energy and finance
The Korean targets sit inside this broader picture. Foreign policy organizations hold sensitive discussions, draft strategy papers and communicate with governments, so they are attractive to anyone seeking political or strategic intelligence.
CrowdStrike also noted that this campaign is distinct from attacks on Korea’s financial sector last month, which likewise involved Artex. Meyers added that several different hacking groups have been seen using the tool over the past six weeks or so. That detail matters: once an AI attack tool exists, it rarely stays with one group.
Why AI Changes the Economics of Hacking
Lower barriers to entry
Meyers pointed out that automating work once done by people has made cyberattacks easier to carry out. Tasks like reconnaissance, probing and follow-up exploitation can now be handled by software running continuously.
Massive scale
A human team can only handle so many victims at once. An AI agent can work through many in parallel. That is how a single group ends up with hundreds of simultaneous targets.
Surprisingly cheap
Researchers estimated that one intrusion attempt by Vapor Panda used roughly 1.4 billion input tokens. Tokens are the units AI models use to process text, and that number would be expensive if bought through a commercial service. But the group may have cut its real spending sharply by running language models on its own inference setup instead of paying per use.
Put together, this means attackers can aim at more victims for less money, and defenders face more attempts than before.
Is This a Brand-New Kind of Attack?
Not exactly, and this is an important point. Meyers stressed that AI-powered hacking is not a completely new category of cyberattack. The techniques are familiar: scanning for flaws, exploiting them, moving deeper into a network. What AI changes is the speed and the volume.
That is encouraging in one sense. If the underlying methods are known, the standard defensive playbook still applies. It simply has to be applied faster and more consistently.
How Organizations Can Defend Themselves
CrowdStrike’s message is that these attacks can still be spotted and stopped when an organization has enough insight into its own environment and monitors threats around the clock. Here is what that looks like in practice.
1. Improve visibility. You cannot protect what you cannot see. Keep an up-to-date inventory of web applications, APIs, servers and cloud services, including forgotten or experimental ones.
2. Monitor continuously. AI agents do not sleep, so defenders cannot rely on office-hours monitoring alone. A 24/7 security operations capability, in-house or outsourced, is now close to essential.
3. Patch web-facing systems quickly. Artex-style tools hunt for weaknesses in public applications and APIs. Shrinking the window between a fix being released and being installed removes easy openings.
4. Secure your APIs. Enforce authentication, rate limits and logging so that repeated automated probing stands out.
5. Use strong identity controls. Multi-factor authentication and least-privilege access limit what an intruder can do even if one door opens.
6. Prepare an incident response plan. Know who to call, how to isolate affected systems and how to notify authorities before a crisis arrives.
7. Fight AI with AI. Defensive tools that use machine learning to spot unusual behavior can help match the pace of automated attackers.
What This Means for Think Tanks, NGOs and Policy Groups
Smaller research institutes and policy organizations often lack big security budgets, yet they hold information that foreign intelligence services want. Cheap, automated attack tools remove the old assumption that only large enterprises are worth the trouble. If an attacker can scan hundreds of targets at almost no extra effort, a modest organization becomes just another entry on the list.
For these groups, basic hygiene matters most: staff training against phishing, tested backups, limited access to sensitive files and a clear plan for reporting suspicious activity.
The Bigger Picture: AI and Cybersecurity in 2026
This episode shows both sides of the AI era. The same technology that helps developers and security teams also helps adversaries. Governments, vendors and companies are all adjusting, and incidents like this one will probably shape new security standards and policy debates.
For readers, the takeaway is practical rather than alarming. AI-assisted attacks are real and growing, but they are beatable with disciplined defense.
Key Takeaways
- Vapor Panda, a China-linked group tracked since 2021, targeted Korean diplomacy and foreign policy organizations, and some attacks succeeded.
- The group used Artex, an AI agent for scanning and exploiting web applications and APIs, mainly powered by DeepSeek.
- An earlier CrowdStrike report said the wider campaign hit more than 200 organizations between October 17 and 29.
- AI makes attacks faster, wider and cheaper, but does not invent entirely new techniques.
- Visibility and 24/7 monitoring remain the strongest defenses.
Final Thoughts
The Vapor Panda campaign is a clear signal that AI-driven cyber operations have moved from theory to everyday practice. Korean foreign policy groups were caught in a worldwide sweep, and the same tools are now spreading among multiple hacking groups. The encouraging part is that the fundamentals still work: know your systems, watch them constantly and respond fast.
Frequently Asked Questions
Vapor Panda is a China-linked hacking group that CrowdStrike has been tracking since 2021. It is considered sophisticated and has recently added AI-driven tools to its operations.
Artex is an AI agent-based penetration testing tool. It repeatedly scans web applications and APIs for weaknesses and then carries out follow-up attack steps automatically based on what it discovers.
CrowdStrike said the targets included think tanks and groups involved in diplomacy and foreign policy, but it did not name specific organizations or reveal how far the breaches went.
According to CrowdStrike, some of the attacks on Korea-related targets did succeed. The affected organizations and the relevant authorities were notified.
CrowdStrike says the group primarily used the Chinese model DeepSeek, and may have supplemented it with paid subscriptions to other advanced AI models.
CrowdStrike reported on November 4 that more than 200 organizations were targeted between October 17 and 29, across Latin America, Europe, Asia, the Middle East and the United States.
No. CrowdStrike’s view is that the methods are largely familiar, but AI sharply increases their speed and scale.
