


Blog
AI Found Bitcoin Node Crash Bugs: What Bitcoin Core’s New Disclosure Policy Means for US Users
29 October 2026
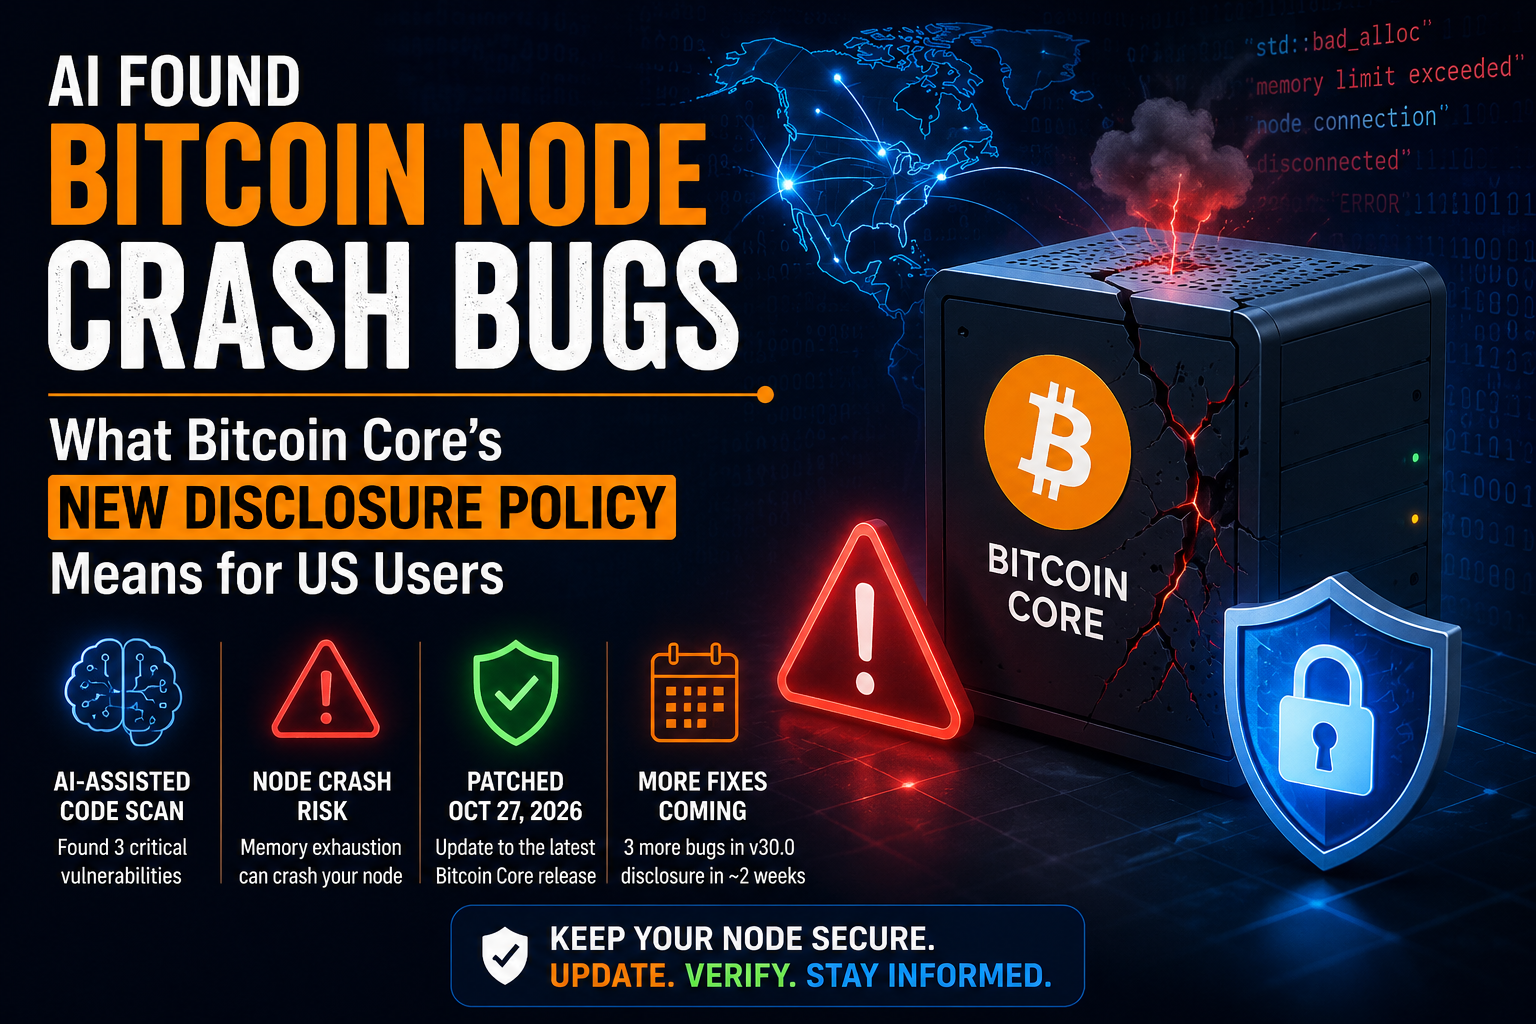
In late October 2026, Bitcoin Core publicly disclosed three vulnerabilities that were first spotted by an AI-assisted code scan. The most serious one let a remote peer overload a node running on Windows, macOS or BSD until it ran out of memory and crashed. Patches were released on October 27, so the fix for US node operators is simple: update to the latest Bitcoin Core release.
Key Takeaways
- A large language model (LLM) scan of Bitcoin Core’s code surfaced three bugs, and human contributors verified each one before it went further.
- The headline flaw could crash nodes on Windows, macOS and BSD through a memory exhaustion attack.
- Bitcoin Core changed its disclosure rules on October 22, 2026. Bugs judged “easily discoverable” are now fixed and announced quickly instead of being held back for months.
- Three more medium and high severity fixes, included in version 30.0, are expected to be disclosed in about two weeks.
- Bitcoin itself, your coins and the blockchain were not reported as compromised. The risk is to individual nodes staying online.
What Happened: AI Meets Bitcoin Core Security
Bitcoin Core is the software most people use to run a full Bitcoin node. A node downloads, checks and relays every transaction and block, which is what keeps the network honest without a central authority.
Developers pointed an LLM-based scanner at the Bitcoin Core codebase. It flagged several weaknesses. Before anything reached the project’s security team, a human contributor reviewed each finding. That human check matters because AI tools can produce false alarms, and the process kept the noise out.
The results were published on October 28, 2026, as three public security advisories.
The Three Vulnerabilities Explained
1. Memory flood that can crash a node (the main one)
The AI scan flagged this issue on October 23. A peer connected to a node running Windows, macOS or BSD could keep sending data until the machine’s memory was exhausted, causing the node to crash. Developers confirmed the problem the same day, and fixes shipped on October 27.
For anyone running a node on a home PC or Mac, this is the one that matters most.
2. Stalling peer that bloats memory
The second flaw was reported to the project on September 15. Interestingly, a different developer found the same issue independently six days later. A connected peer could pretend to run an outdated protocol version and then simply stop responding. Messages then piled up in the victim’s memory, growing by up to about 2MB per hour on each incoming connection and about 5MB per hour on each outgoing one, according to the advisory.
It is slow, but on a node left running for days or weeks, it adds up.
3. Block file overflow (low severity)
The third bug was rated low severity but was reported three times: once by the AI scan and twice by human developers, in August and on October 23. In theory, a miner could craft blocks that overflow the files a node keeps to handle a chain reorganization, which is when the network swaps a few recent blocks for a competing set.
On 64-bit systems, pulling this off would take roughly a month of the entire network’s block production, so it is mostly theoretical. On Windows and 32-bit systems, though, a node can fail completely, and restarting does not fix it. Nodes on 32-bit hardware or on older FAT32-formatted drives remain exposed even after the patch.
Why Bitcoin Core Changed Its Disclosure Rules
For years, the project often kept medium severity bugs quiet for up to a year. The idea was to give operators time to upgrade before attackers learned where to look.
AI changed that math. If a language model can find a bug cheaply, so can anyone else, including people with bad intentions. The second bug above proves the point, since two separate people found it within a week. On October 22, 2026, Bitcoin Core adopted a new approach for easily discoverable bugs: ship fixes fast to every supported version and publish an advisory right away.
This is a real shift in how open-source security is handled, and it is likely to influence other crypto and software projects.
What This Means for Users in the United States
Home node operators. Many US hobbyists and privacy-focused users run nodes on Windows or Mac machines, which are exactly the systems affected by the main flaw. If this is you, update now.
Businesses and developers. If your company runs Bitcoin Core for payments, wallets, analytics or exchange infrastructure, a crashing node can mean downtime and missed transaction data. Add Bitcoin Core advisories to your regular security monitoring.
Miners and mining pools. Check that your setup uses 64-bit hardware and a modern file system, since the third bug hits older configurations hardest.
Everyday Bitcoin holders. If you only use an exchange or a hardware wallet, you do not need to take action. This is a node software issue, not a theft vulnerability.
How to Protect Your Bitcoin Node: A Simple Checklist
- Update Bitcoin Core to the latest patched release from the project’s official site.
- Verify the download using the published signatures and checksums before installing.
- Confirm you are on 64-bit hardware and avoid FAT32 drives for block storage.
- Watch for the next disclosure. Three more bugs fixed in version 30.0 are due to be made public in around two weeks.
- Monitor your node’s memory use. Sudden growth can be an early warning sign.
- Subscribe to official security advisories so you hear about issues from the source, not from rumors.
The Bigger Picture: AI Is Now Part of Cybersecurity
This story is less about three bugs and more about a trend. AI tools are getting good at reading large codebases and spotting flaws that humans missed or had not yet reviewed. That helps defenders, but it also helps attackers, which is why faster disclosure is becoming the practical answer.
Expect more open-source projects, in crypto and beyond, to rethink how long they can afford to keep bugs secret.
Frequently Asked Questions
Yes. An LLM-based scan of the codebase flagged three vulnerabilities, which human contributors then verified and the security team fixed before public disclosure.
No theft was reported. The flaws affect node stability, meaning they can crash or stall node software. Your coins are not at risk from these bugs.
The main memory flood bug affected nodes on Windows, macOS and BSD. The block file issue is also more serious on Windows and 32-bit systems.
Update to the latest patched Bitcoin Core release, verify the download, and check that your hardware and storage are modern 64-bit setups.
Since October 22, 2026, bugs considered easy to discover, especially with AI tools, are fixed and disclosed quickly with a public advisory instead of being kept secret for up to a year.
Yes. Three additional medium and high severity bugs fixed in version 30.0 are expected to be disclosed in about two weeks.
The reports describe node-level risks, not a break in the Bitcoin protocol. Nothing in the advisories suggests the network itself is under threat.
Yes, as long as you keep your software updated. Running a node remains one of the best ways to verify the network independently.
